https://www.xserver.ne.jp/news_detail.php?view_id=19987
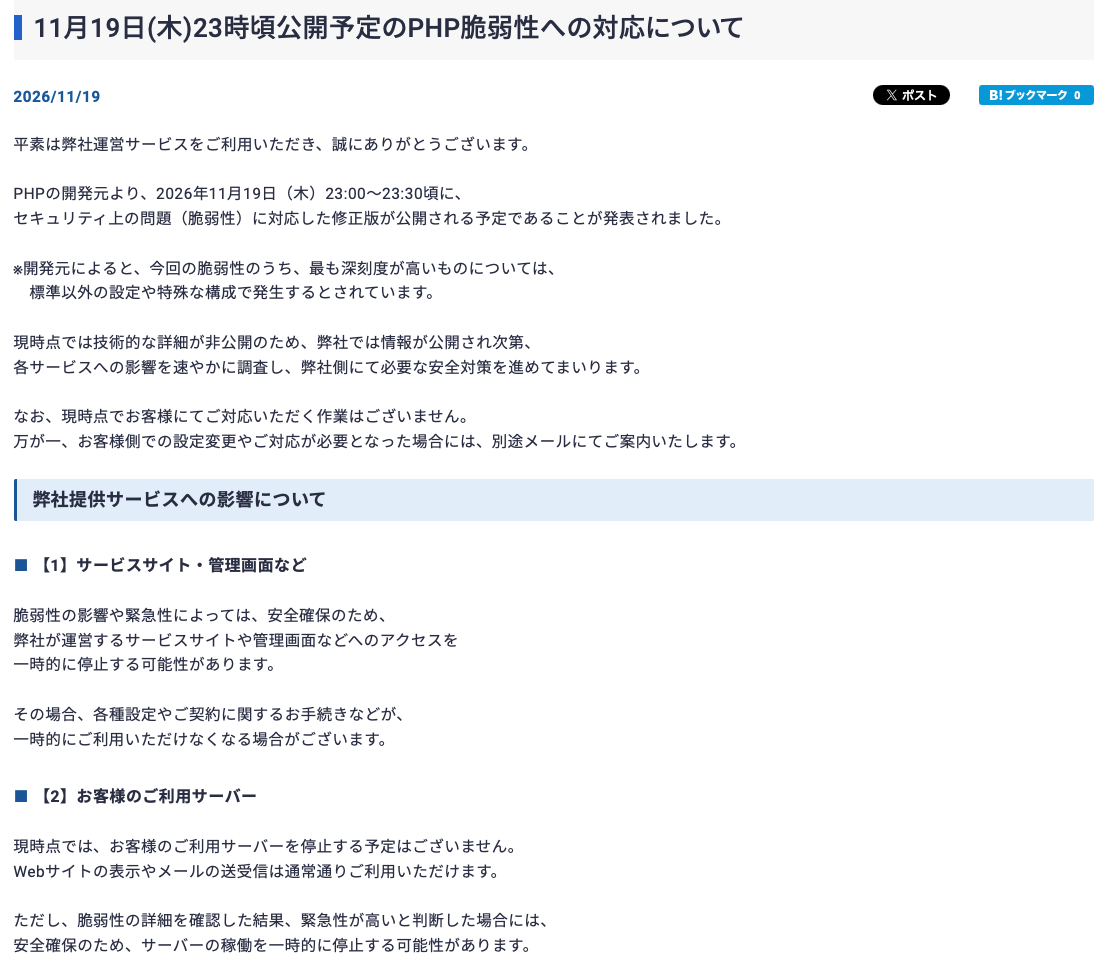
PHPの開発元より、2026年11月19日(木)23:00〜23:30頃に、セキュリティ上の問題(脆弱性)に対応した修正版が公開される予定であることが発表されました。
※開発元によると、今回の脆弱性のうち、最も深刻度が高いものについては、標準以外の設定や特殊な構成で発生するとされています。
2026年11月19日23時時点では、XServerサーバ管理画面にてPHPバージョンの新しい選択肢は提供されていまん。
深刻度は「標準以外の設定や特殊な構成」の場合にクリティカル(重度)とされています。
弊社管理サイトにおいては基本的に標準設定となっているため影響は小さいと思われますが、サーバにて対策され次第アップデート及びサイトのエラー確認を行います。
8.3.37リリースされました
https://www.php.net/archive/2026.php#2026-11-19-2
PHP開発チームは、PHP 8.3.37のリリースを発表しました。これはセキュリティリリースです。
PHP 8.3をご利用のすべてのユーザーに対し、本バージョンへのアップグレードを推奨します。
PHP 8.3.37のソースコードは、ダウンロードページから入手可能です。同ページでは、Windows向けのソースコードおよびバイナリも提供されています。変更点の詳細は、ChangeLog(変更履歴)をご確認ください。
Change Log
Version 8.3.37
19 Nov 2026CGI:Fixed GHSA-5j3f-64r7-f564 (PHP-CGI out-of-bounds read and write during PATH_INFO correction). (CVE-2026-129538)
Date:Fixed GHSA-gr4f-wgx5-jpfv (Timezone cache use-after-free can lead to remote code execution). (CVE-2026-129496)
FPM:Fixed GHSA-qc49-hpvq-g2w6 (PHP-FPM request smuggling through an unread HTTP request body). (CVE-2026-129289)
Fixed GHSA-3mg3-cr28-46gc (PHP-FPM status endpoint XSS via unescaped user and script fields). (CVE-2026-129292)
Fixed GHSA-jm4m-qfqx-967m (PHP-FPM epoll use-after-free can lead to local privilege escalation). (CVE-2026-129291)
Phar:Fixed GHSA-68fq-fh7h-f8gr (PHAR OpenSSL signature bypass via algorithm downgrade). (CVE-2026-128090)
Session:Fixed GHSA-fm2m-fjf5-v3cp (Partially overwritten session files can lead to remote code execution). (CVE-2026-126714)
Fixed GHSA-658j-r8rw-q6mx (Session serializer mismatch can lead to remote code execution). (CVE-2026-115560)
Fixed GHSA-g3vh-838c-65v7 (Use-after-free after interrupted session shutdown). (CVE-2026-129481)
SOAP:Fixed GHSA-q23r-hr55-xmpg (SOAP information disclosure through malformed array dimensions). (CVE-2026-15353)
Fixed GHSA-4646-p932-gw34 (SOAP use-after-free when processing DTD entity references). (CVE-2026-129506)
Standard:Fixed GHSA-f6gg-rchx-xw8j (Mixed-case HTTPS and FTPS URLs can expose data in plaintext). (CVE-2026-128064)
Fixed GHSA-mmf9-xm3v-hg2x (Denial of service through folded HTTP response headers). (CVE-2026-127960)
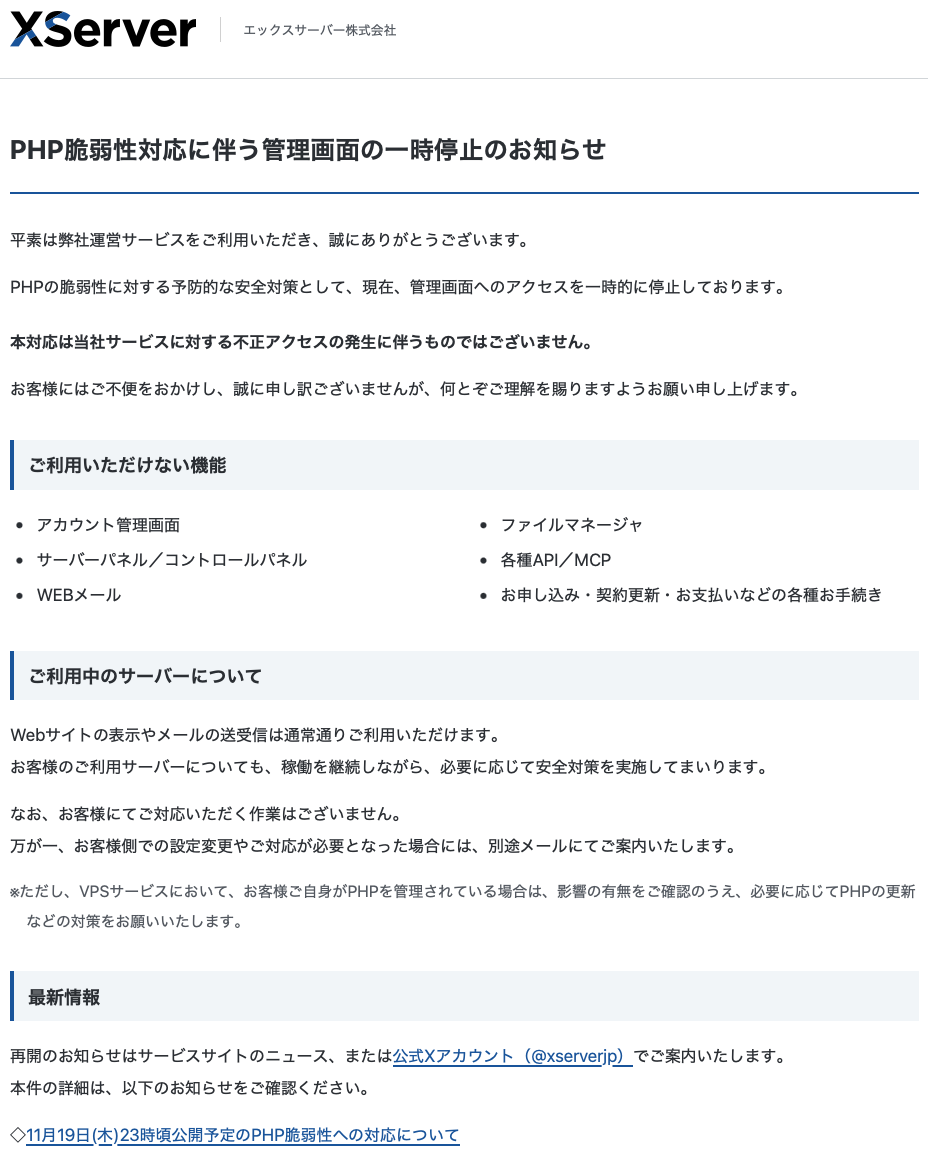
XServer管理画面は操作不能(対処中)